npmscan.com
Is the npmscan.com MCP server safe to use?
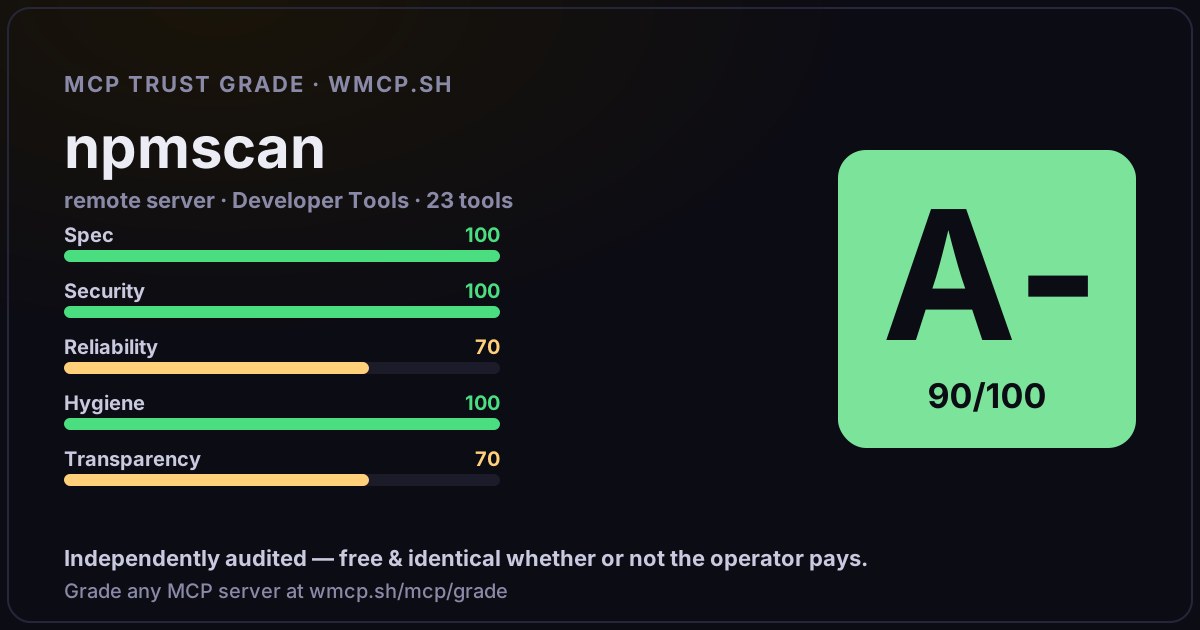
Independent trust grade A- (90/100). No blocking issues found in the static + spec checks. wmcp.sh continuously watches npmscan.com for tool drift and rug-pulls. The grade is free and identical whether or not the operator pays.
What it offers — 23 tools · Developer Tools
search_packagesSearch the npm registry by name or keywords. Each result includes its current weekly/monthly download counts, dependentsCount (how many other npm pack
get_packageFetch npm registry metadata for a package: latest version, install scripts (preinstall/postinstall are a key risk signal), maintainers, license, recen
get_package_versionFetch registry metadata for one exact version of a package (dependencies, install scripts, tarball) AND check that exact version against OSV.dev for k
get_maintainer_profileGiven an npm username, returns every package npm's own maintainer:<username> search index currently returns for that account (registry.npmjs.org's /-/
query_vulnerabilitiesQuery OSV.dev for known vulnerabilities affecting an npm package, optionally scoped to one exact version (e.g. to check whether a version pinned in a
batch_query_vulnerabilitiesQuery OSV.dev for known vulnerabilities across a whole npm dependency inventory at once: either pass a flat {packages:[...]} list, or paste raw packag
get_latest_advisoriesBrowse recently published npm security advisories and known-malicious-package findings. Three disjoint sources, selected via type: "reviewed" (default
get_cveLook up authoritative NIST NVD data for one exact CVE ID (e.g. "CVE-2026-2950"), or browse/search NVD by keyword, CVSS severity, CWE, or a publication
analyze_install_scriptStatically scans a package's preinstall/install/postinstall/prepare lifecycle scripts AND the file(s) they reference — fetched directly from the publi
analyze_transitive_dependenciesRecursively resolves one or more direct/root packages' dependency graphs — e.g. the "dependencies" section of a package.json — up to maxDepth levels d
check_package_provenanceChecks whether a package version was published with npm's own Sigstore-backed publish provenance (`npm publish --provenance`), and cross-checks that p
check_maintainer_changesReconstructs a package's maintainer-change history straight from the npm packument — every published version carries the maintainers-list SNAPSHOT as
check_maintainer_blast_radiusGiven an npm username, finds every package npm's own maintainer:<username> search index currently returns for that account (registry.npmjs.org's /-/v1
check_license_complianceGiven a list of packages (name + optional exact version or semver range — e.g. straight from a package.json "dependencies" object) and an optional all
diff_dependenciesCompares two raw snapshots of a package.json, package-lock.json (npm v1-v3), yarn.lock (classic v1 or Berry), or pnpm-lock.yaml — e.g. before/after a
prioritize_remediationGiven a batch of vulnerability findings already flagged elsewhere (e.g. from batch_query_vulnerabilities, analyze_transitive_dependencies, or query_vu
simulate_dependency_upgradeGiven a package and a current/target version, tells you whether that specific upgrade is a safe patch/minor bump or a likely-breaking major bump, befo
suggest_alternativeGiven a package that looks deprecated, vulnerable, abandoned, or suspicious, suggest better-maintained alternatives in the same category. This tool fi
+5 more tools
- ✓ initialize → protocolVersion 2025-06-18
- ✓ initialize HTTP 200
- ✓ unknown method → -32601
- ✓ tools/list → 23 tools
- ✓ every tool has name + inputSchema
- 23 tools scanned
- no injection markup
- no secret-path refs
- single-probe latency 1809ms (PRELIMINARY — continuous uptime/p95 from proxy telemetry lands in v2)
- 100% of tools have typed inputSchema
- 23/23 declare outputSchema
- no unannotated destructive tools
- HTTPS ✓
- advertises protocol 2025-06-18
Observed behavior
No proxied traffic observed for this host yet. Connect it at /connect and its grade gains a measured Reliability score + per-tool behavioral evidence — the half a static scan can't produce.
Findings
We re-grade npmscan.com on a schedule and alert your Slack/webhook the moment its tools change or its grade drops — rug-pull insurance for the connection.
Run npmscan.com? Claim it (free) to get drift alerts and show an independently-verified trust badge. The grade stays free — claiming just ties it to you.
Share this report card
A 1200×630 card with the grade + audit — drop it in a post, Slack, or your repo.
Embed this grade
A live badge — it re-verifies itself and shows current stability. Static scorecards can't. Paste it in your README or site to show users you're independently audited.
[](https://wmcp.sh/mcp/grade/npmscan.com)
<a href="https://wmcp.sh/mcp/grade/npmscan.com"><img src="https://wmcp.sh/mcp/grade/npmscan.com/badge.svg" alt="MCP Trust Grade A- · wmcp.sh"></a>
Agents: check this before connecting
Add the wmcp.sh trust oracle as an MCP server and call grade_mcp_server / check_mcp_drift in your agent's pre-connection gate:
https://wmcp.sh/mcp/trust
readOnly vs observed behavior) layer on via the wmcp.sh proxy.